A vendor management audit assesses how well an organization controls vendor relationships from the initial request through final offboarding.
For large enterprises, vendor information changes frequently. Manual work makes those changes harder to manage. IFOL’s 2025 AP research found that 66% of AP teams still manually enter invoice data into ERP systems, creating more room for supplier record errors, payment exceptions, and audit issues.
A strong vendor management audit helps procurement, finance, AP, risk, and compliance teams identify these issues before they become overpayments, fraud exposure, compliance issues, and weaker third-party risk management.
In this guide, we’ll explain what a vendor management audit includes, how it differs from an AP recovery audit, and how enterprises can use audit findings to improve supplier risk management.
Key Takeaways:
- A vendor management audit checks how a company manages vendors: It reviews how vendors are approved, paid, monitored, reviewed, and offboarded. The goal is to make sure vendor relationships follow company rules, contract terms, payment controls, and risk requirements.
- Bad supplier data can create bigger problems: Duplicate vendor records, missing tax details, outdated payment terms, unverified bank accounts, and inactive vendors can lead to payment errors, compliance issues, and weak supplier oversight.
- Vendor audits help find payment mistakes: A vendor management audit can help teams spot duplicate payments, missed credits, overpayments, pricing errors, and contract mismatches. It also helps teams understand what caused those issues.
- Audit findings should lead to action: Findings should help teams update supplier risk scores, review schedules, approval rules, payment controls, document requirements, and remediation plans.
- apexanalytix helps enterprises act on audit findings: apexanalytix supports vendor management audits with supplier data validation, vendor master review, bank account validation, duplicate vendor and payment detection, AP recovery audit support, continuous monitoring, and AI-powered risk workflows.
What Is a Vendor Management Audit?
A vendor management audit is a structured review of how a company approves, tracks, pays, monitors, and controls its vendors.
It helps confirm that vendor relationships follow internal policies, contract terms, payment controls, compliance requirements, and third-party risk management standards.
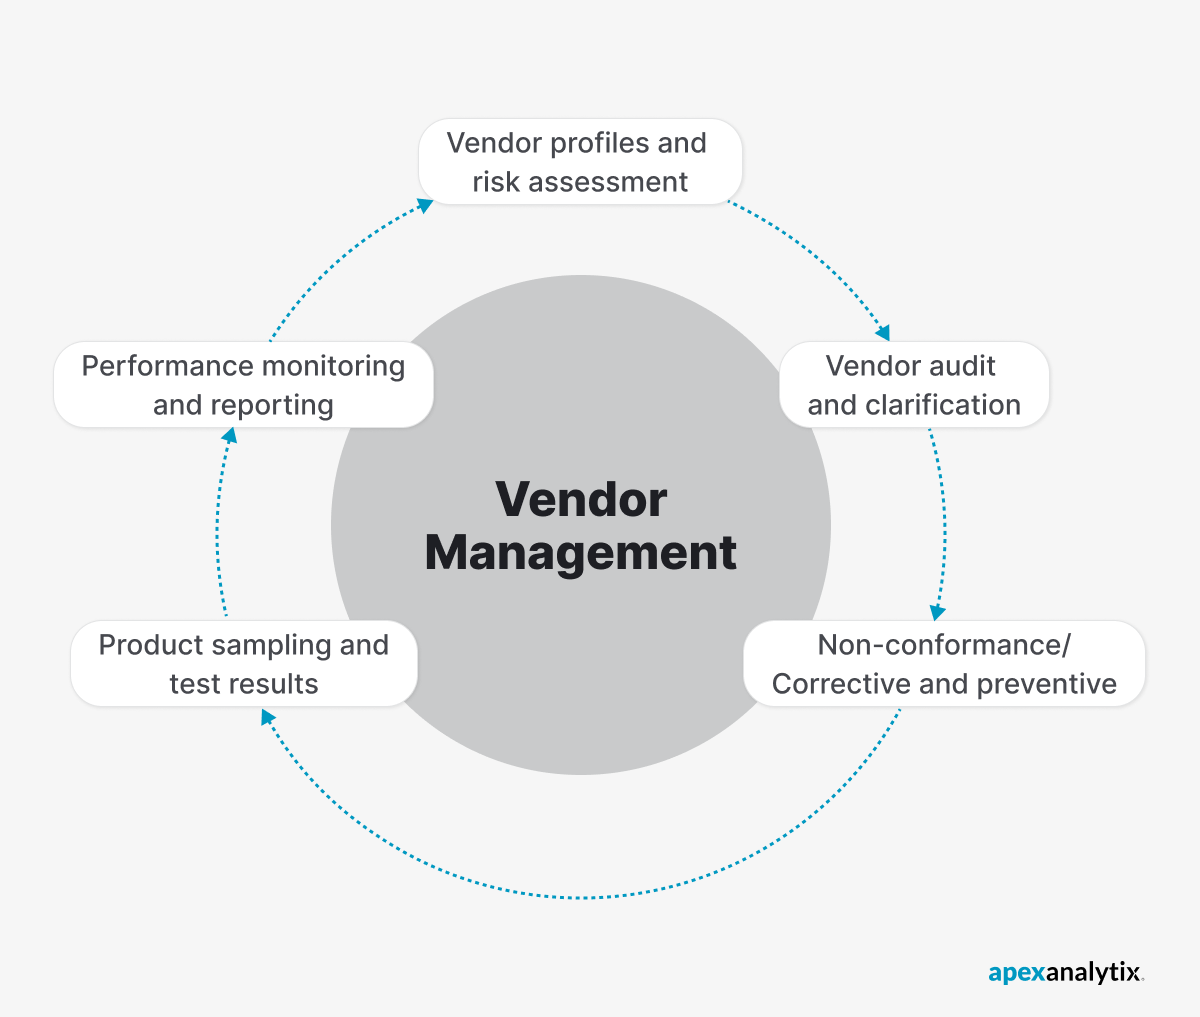
The audit reviews the full vendor lifecycle, from initial request and onboarding to ongoing monitoring, issue resolution, and offboarding. It also tests the process behind those records.
A vendor management audit connects those activities into one clear view. It helps the business answer practical questions:
- Who approved the vendor?
- What checks happened before activation?
- Do contract terms match payment activity?
- Are high-risk vendors reviewed more often?
- Has the business resolved open credits, disputes, or compliance issues?
- Are inactive or terminated vendors fully closed out?
A strong audit helps teams find weak approval steps, missing documents, outdated risk reviews, payment control issues, duplicate records, and unresolved vendor problems.
Why Vendor Management Audits Matter
Vendor management audits help enterprises keep supplier data accurate, payments controlled, risks visible, and compliance evidence up to date.
1. Protects supplier data accuracy
Supplier data affects approvals, payments, reporting, risk scoring, and compliance reviews. When that data is wrong, small errors can move through multiple systems.
Common issues include:
- Duplicate supplier records
- Incorrect legal names
- Missing tax details
- Outdated addresses
- Unverified bank accounts
- Incorrect payment terms
- Inactive vendors still open for payment
A vendor management audit helps correct vendor master data before bad data causes payment, reporting, or compliance problems.
2. Reduces payment errors and recoverable losses
Large enterprises process high volumes of invoices across many vendors, ERPs, currencies, and business units. That makes payment errors harder to catch.
A vendor management audit can help identify:
- Duplicate payments
- Overpaid invoices
- Missed credits
- Unapplied supplier refunds
- Payments to inactive vendors
- Pricing, freight, tax, or contract errors
The audit connects payment issues to the vendor record, contract term, approval step, or control that caused them. That helps teams recover losses and prevent repeat errors.
3. Strengthens supplier risk management
Supplier risk changes over time. A vendor may update bank details, lose insurance coverage, miss compliance requirements, create repeated invoice exceptions, or leave disputes unresolved.
A vendor management audit helps teams decide what action to take, such as:
- Requesting updated documents
- Validating a bank change
- Updating a supplier risk profile
- Placing a payment hold
- Starting a remediation plan
- Reviewing high-risk vendors more often
4. Improves compliance oversight
Compliance teams need current evidence that vendors comply with company policies, contractual requirements, and regulatory standards.
A vendor management audit can show:
- Which vendors completed due diligence
- Which documents are missing or expired
- Which contracts need review
- Which suppliers need updated tax, insurance, or certification records
- Which compliance issues remain unresolved
5. Protects business continuity and reputation
A vendor issue can quickly become an operational issue.
According to ISC2’s 2025 supply chain risk survey, 34% of enterprise organizations experienced a cybersecurity incident that originated from a third-party vendor or supplier over the past two years.
A vendor management audit helps leaders identify suppliers that need closer review before small issues turn into larger disruptions. It shows which vendor problems could affect operations, reputation, customer trust, or business continuity.
6. Supports better business decisions
Vendor management audits give leaders practical evidence they can act on.
The findings help:
- Procurement improve supplier oversight
- Finance find recovery opportunities
- AP fix process weaknesses
- Risk teams update supplier reviews
- Compliance teams confirm required controls
The value of a vendor management audit is simple: cleaner data, fewer payment errors, stronger controls, and better decisions across the vendor base.
Vendor Management Audit vs. AP Recovery Audit
A vendor management audit and an AP recovery audit support different parts of supplier control.
A vendor management audit reviews the supplier lifecycle, including onboarding, vendor records, contracts, compliance documents, risk status, payment controls, issue tracking, and offboarding.
An AP recovery audit reviews accounts payable activity to find recoverable losses, such as duplicate payments, missed credits, unapplied credit memos, overpayments, and pricing or contract errors.
| Area |
Vendor Management Audit |
AP Recovery Audit |
| Main focus |
How the business manages vendors across the full supplier lifecycle |
Where AP activity created recoverable financial loss |
| What it reviews |
Onboarding, vendor records, contracts, compliance documents, risk status, payment controls, issue tracking, and offboarding |
Invoices, payments, credits, supplier statements, pricing, contract terms, and payment history |
| Primary goal |
Improve supplier control, reduce vendor risk, and strengthen governance |
Recover overpayments, missed credits, unapplied credit memos, and other financial leakage |
| Common findings |
Duplicate vendor records, missing documents, outdated risk reviews, weak approval steps, and inactive vendors still open for payment |
Duplicate payments, overpayments, missed credits, pricing errors, contract mismatches, and unapplied refunds |
| Main teams involved |
Improve supplier control, reduce vendor risk, and strengthen governance |
AP, finance, recovery audit, procurement, and internal audit |
| Best outcome |
More accurate supplier data, stronger controls, and better vendor oversight |
Recovered cash, stronger AP controls, and fewer repeat payment errors |
What Does a Vendor Management Audit Include?
A vendor management audit includes the records, controls, and review points that show how a vendor moves through the business.
The scope should cover the full relationship, but the audit should focus on evidence, ownership, and control quality rather than simply verifying that documents exist.
| Checklist area |
What to review |
| Vendor identity |
Supplier name, legal entity, address, parent company, status, and approval history |
| Tax and legal details |
Tax IDs, W-9 or W-8 forms, licenses, ownership details, and required legal records |
| Bank account details |
Payment instructions, bank validation, recent changes, approvals, and verification evidence |
| Contract terms |
Payment terms, renewal dates, pricing rules, discounts, SLAs, and termination clauses |
| Payment history |
Invoice activity, payment timing, exceptions, duplicate payments, and overpayments |
| Supplier statements |
Open credits, refunds, debit balances, statement differences, and recovery opportunities |
| Risk reviews |
Risk ratings, review dates, supplier criticality, ownership changes, and issue history |
| Compliance documents |
Insurance, certifications, sanctions checks, expiration dates, and open compliance items |
| Offboarding status |
Inactive vendor closure, removed payment access, final issues, and open balances |
| Remediation tracking |
Owner, action, deadline, control update, and evidence of resolution |
How to Conduct a Vendor Management Audit
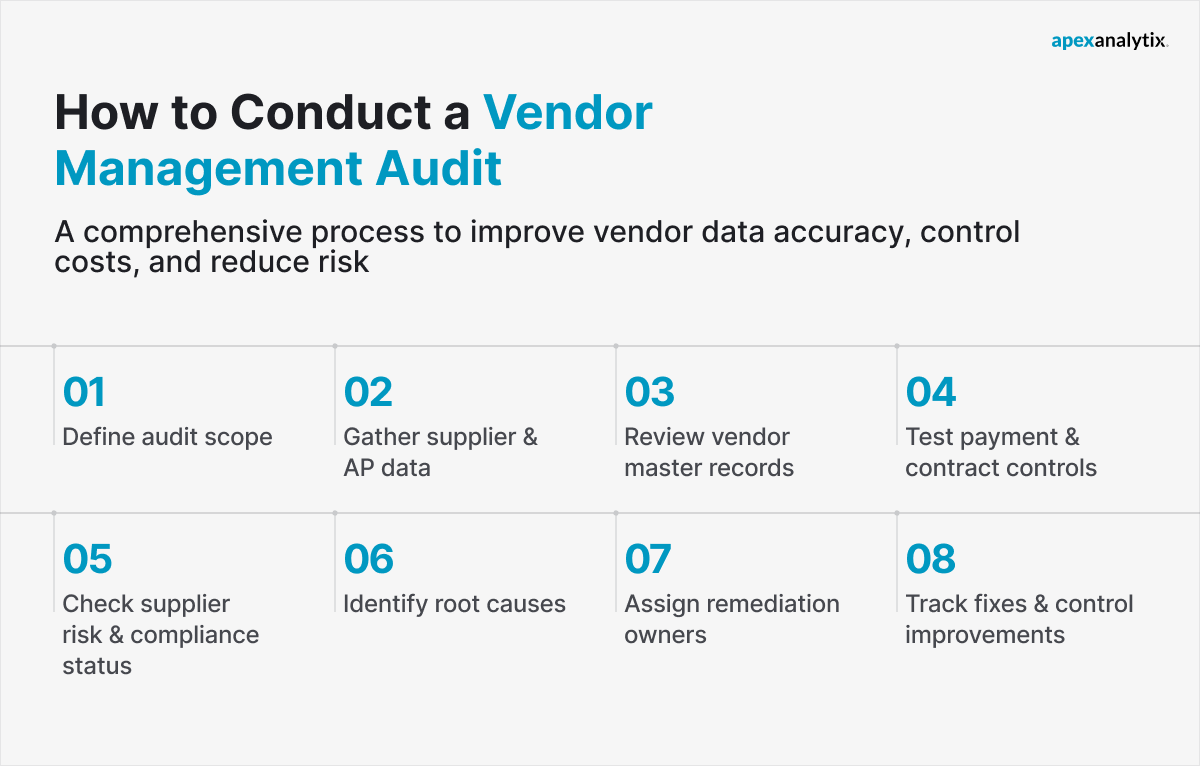
A vendor management audit should follow a structured process that moves from scope to findings, remediation, and control improvement:
1. Define the audit scope
Start by deciding which vendors, systems, business units, and time period the audit will review.
Gartner reports that 40% of compliance leaders say 11%-40% of their third parties are high-risk. That makes risk-based scoping important for vendor management audits.
Prioritize vendors with:
- High payment volume
- Critical business impact
- Recent bank account changes
- High-risk status
- Unresolved disputes or compliance issues
- Inactive status but open payment access
The scope should also define the audit objective. One audit may focus on vendor master accuracy, while another may focus on payment controls, compliance readiness, supplier risk, or recovery opportunities.
2. Gather supplier and AP data
Pull the records needed to review each vendor relationship across supplier management, ERP, AP, contract, and risk systems.
The audit file should include:
- Vendor master records
- Onboarding files
- Contracts and payment terms
- Risk reviews
- Invoice and payment history
- Supplier statements
- Change logs
- Open issue records
A single working file helps teams compare vendor details, payment behavior, contract terms, and risk indicators in one place. It also makes it easier to spot issues that one department may miss when reviewing its own data.
3. Review vendor master records
Review the vendor master for fields that affect payments, reporting, risk review, and compliance.
The review should flag records that need correction, including:
- Duplicate vendor profiles
- Missing tax details
- Incomplete ownership information
- Outdated payment terms
- Inactive vendors still open for payment
- Supplier records with missing approval history
4. Test payment and contract controls
Compare actual payment activity against approved contract terms, payment terms, discount rules, tax requirements, and payment instructions.
The goal is to confirm that the business pays vendors according to approved terms.
Look for patterns such as:
- Invoices paid under outdated terms
- Credits left open
- Pricing that does not match the contract
- Payment changes without enough review
- Transactions that bypass approval rules
- Repeated invoice exceptions from the same supplier
These findings show where the process broke down and where AP controls need improvement.
5. Check supplier risk and compliance status
Review current risk and compliance records for vendors in scope, especially critical suppliers and vendors with access to systems, sensitive data, payment flows, or regulated processes.
McKinsey reports that technology supply chains contributed to nearly one-third of cyber breaches over the past two years.
Pay close attention to changes since onboarding, such as:
- New ownership
- Expired documents
- Recent bank updates
- Repeated invoice exceptions
- Unresolved incidents
- Higher operational or compliance risk
- New system or data access
6. Identify root causes
After the audit team finds an issue, it should trace the issue back to the cause.
Common root causes include weak onboarding checks, unclear approval rules, poor vendor master governance, disconnected systems, missing ownership, or too much manual AP work.
Root-cause analysis helps teams avoid temporary fixes. For example, closing one duplicate record solves the immediate issue, but improving duplicate detection helps prevent the same problem from returning.
7. Assign remediation owners
Every audit finding should have an owner, a deadline, and a next step.
Procurement, AP, finance, compliance, legal, risk, or IT may own different parts of the fix depending on the issue.
Strong remediation tracking should answer:
- Who owns the fix?
- What action needs to happen?
- When should the business confirm completion?
- Which control needs to change?
- What evidence shows the team resolved the issue?
8. Track fixes and control improvements
Track each finding until the business confirms the correction. The audit team should record the action taken, the owner, the completion date, and the evidence that shows the team resolved the issue.
The final audit output should show what the team found, what it fixed, what remains open, and which controls need improvement.
A strong audit leaves the business with more accurate records, stronger ownership, and fewer repeat issues across the vendor base.
How apexanalytix Helps Turn Vendor Management Audits Into Action
Vendor management audits often uncover issues across supplier data, payments, compliance records, and risk controls. To create lasting value, teams need to connect those findings with the systems and workflows that manage vendors every day.
apexanalytix supports that process with supplier management technology, AP recovery audit expertise, continuous monitoring, and AI-powered risk workflows.
Key features that support vendor management audits include:
- Supplier data validation: Validates supplier data against 1,200+ trusted data sources to support stronger onboarding, approval, compliance, and payment decisions
- Vendor master accuracy: Helps teams identify outdated, incomplete, duplicate, or inconsistent supplier records across large vendor populations
- Bank account validation: Reviews bank account ownership, entity matches, account standing, and other risk signals before payment details change
- Duplicate vendor and payment detection: apexanalytix uses AI and advanced analytics to find duplicate suppliers, duplicate payments, missed credits, outliers, and recovery opportunities
- AP recovery audit support: Helps finance and AP teams recover overpayments, missed vendor credits, unapplied credit memos, and pricing or contract discrepancies
- Continuous supplier monitoring: Tracks supplier changes, prohibited list matches, compliance events, negative news, financial risk, cyber risk, and other vendor risk signals over time
- Supplier risk management workflows: Helps procurement, finance, AP, risk, compliance, legal, and IT teams act on findings with stronger ownership and remediation tracking
Case study: Global healthcare leader strengthens supplier compliance and risk management
apexanalytix helped a global healthcare enterprise manage supplier compliance and risk across 250,000+ suppliers, 600+ legal entities, $27B+ in supplier spend, and 80+ ERP systems.
The company used apexanalytix to standardize supplier onboarding, automate compliance and verification processes, improve supplier data governance, and enable continuous supplier risk monitoring.
For vendor management audits, that example shows why enterprises need accurate supplier data, consistent controls, and ongoing visibility across the full vendor lifecycle.
Together, these capabilities help enterprises move from one-time vendor review to stronger supplier control, payment protection, and risk management.
Need a better way to turn vendor management audit findings into stronger supplier controls?
Contact apexanalytix to see how its supplier data validation, AP recovery audit support, continuous monitoring, and AI-powered risk workflows can help your enterprise reduce vendor risk and improve payment control.
FAQ
1. How often should enterprises run vendor management audits?
Enterprises should run vendor management audits at least annually, with more frequent reviews for high-risk suppliers, critical vendors, recent bank account changes, major ERP changes, M&A activity, or suppliers with unresolved issues.
2. Who is responsible for a vendor management audit?
Vendor management audits usually involve procurement, finance, AP, risk, compliance, legal, and internal audit. Procurement often owns supplier relationships, while finance and AP review payments, risk teams assess exposure, and compliance confirms required controls and documents.
3. How do vendor audit findings improve supplier risk management?
Vendor audit findings can update supplier risk scores, review frequency, approval rules, payment controls, documentation requirements, and remediation plans. They help teams turn audit issues into practical risk actions instead of leaving findings in a report.